This guide explains how Havi Nextgen is evaluated in real projects—covering typical pricing structures, supplier considerations, and the practical requirements that affect selection. It then provides objective background on the keyword and related procurement themes, helping readers compare options methodically based on compatibility, support readiness, and delivery terms rather than marketing claims.
If you’re evaluating Havi Nextgen, the fastest path to a sensible decision is to start with three practical checkpoints: (1) fit for your workflow, (2) implementation and support capability, and (3) total cost of ownership—not just the upfront price. Many purchasing teams discover that the biggest cost and schedule risks come from mismatched requirements, unclear responsibilities between buyer and supplier, and weak documentation for deployment.
In practice, “fit for your workflow” is where most misunderstandings begin. Teams often assume that because a platform is “next-generation,” it will naturally match their processes. But workflow fit is about details: what your users need to do day-to-day; how approvals flow; what exceptions look like; how data is entered, validated, and corrected; and how reporting or auditing must behave under real-world conditions. When these are not captured early, procurement decisions become technically optimistic and operationally fragile.
Then comes “implementation and support capability.” Even a product that is technically strong can fail operationally if the supplier’s delivery method is weak, the handover is incomplete, or the support model doesn’t match how incidents occur in your organization. Procurement teams should therefore ask: can this supplier deliver a stable rollout that your operations team can maintain without heroics?
Finally, “total cost of ownership” is the third checkpoint that prevents budget surprises. The upfront quote rarely represents the entire cost of deployment. Operational overhead—training time, governance activities, monitoring and incident handling, integration maintenance, and update cycles—can exceed initial implementation costs in some environments.
In this guide, “pricing” and “supplier” topics are treated objectively: we discuss what usually drives cost, what procurement questions matter very, and which conditions typically appear in a competent vendor proposal. This approach is designed to help you compare suppliers and configurations with fewer surprises.
Procurement leaders often research Havi Nextgen because next-generation platforms and systems tend to promise better scalability, faster configuration, and more consistent delivery standards. In many organizations, modernization initiatives are also aligned with vendor lifecycle pressures: older platforms may be reaching end-of-life, or they may no longer meet security expectations, scalability needs, or integration requirements.
However, the actual value of next-generation platforms is rarely automatic. It depends on adoption context—how the product integrates with existing tooling, how your team is trained, and how ongoing updates are handled. A platform can be technically impressive but still create operational burden if it requires extensive customization without support pathways, or if it uses patterns that conflict with your existing identity, logging, or data governance models.
From an industry-expert procurement lens, the question is rarely “Is it modern?” Instead, it’s “Is it operationally compatible with our current environment, and can we govern it responsibly once it’s live?” That viewpoint keeps evaluations grounded and helps avoid selecting a technically impressive option that becomes difficult to operate.
Operational compatibility includes items procurement teams sometimes underestimate:
These points turn “procurement interest” into “procurement readiness,” which is the real goal when evaluating Havi Nextgen.
When buyers search for Havi Nextgen pricing, they often encounter multiple proposal formats. While exact figures vary widely by region, scope, and contract terms, the very common cost drivers include:
Expert note: A “low upfront” quote can be misleading if it omits integration, training, or operational readiness activities. Conversely, a higher quote may be justified if it includes measurable acceptance testing, robust documentation, and a clear handover plan.
To make pricing evaluations objective, procurement teams should treat vendor pricing as a structured bundle of decisions—not a single number. A quote that is cheaper may be cheaper because it assumes you will do more work internally, because it excludes certain modules, because it excludes specific security or audit needs, or because it understates post-go-live support.
Below are common “hidden” or “often excluded” components that frequently show up only after procurement questions:
Reliable sourcing approach: Because pricing is contract-specific, this guide avoids inventing numbers. For benchmarking, procurement teams should request itemized proposals and compare on the same line items, not on total totals alone. If you want, share your intended scope (industry, number of sites/users, desired timeline) and I can provide a structured comparison checklist.
One practical technique is to build a “pricing decomposition spreadsheet” that uses consistent categories across vendors—licenses, implementation phases, integration tests, data migration tasks, training bundles, support tiers, and optional enhancements. This allows teams to see which vendor is actually providing more value versus which vendor simply priced fewer components.
The supplier question is where many projects succeed or struggle. In Havi Nextgen selection, evaluate suppliers on evidence of operational readiness rather than only on product claims. Key supplier criteria typically include:
Practical recommendation: Ask for a sample project plan and an example of how they handle post-go-live issues. A competent supplier will usually provide a transparent view of timelines, risks, and responsibilities.
It’s also useful to examine “supplier readiness” through how they respond to detailed questions. When procurement asks about acceptance testing, data migration reconciliation, or support escalation logic, a capable supplier will typically do more than promise. They will explain how they will execute, what evidence they produce, which roles they assign, and what the buyer must prepare.
Supplier evaluation can be structured into four layers:
To further assess maturity, procurement teams often request references or evidence from similar deployments: comparable system size, comparable integration complexity, and similar timelines. Equally important is the quality of those references: not just a “yes we succeeded,” but details about how risks were handled.
One more supplier-evaluation step that tends to pay off: ask how the supplier would handle a scenario where the acceptance test fails or where an integration behaves differently than expected under load. The answer tells you whether the supplier has a controlled, repeatable approach to recovery—or whether they rely on improvisation.
Even when the technology is a strong match, projects can stall if requirements are vague. Below are conditions that frequently appear in credible supplier proposals for next-generation deployments—use them as a readiness checklist for your Havi Nextgen evaluation.
Objective framing: These items reflect common industry project-management patterns. Your exact requirements will depend on your internal standards and regulatory obligations.
Acceptance is not merely a signature on paperwork; it’s a structured confirmation that the system meets agreed expectations. The strongest proposals usually include:
Additionally, acceptance can be hindered by missing “dependency readiness.” If the platform depends on data quality improvements, identity configuration, or network rules that are controlled by other teams, procurement should ensure the supplier plan explicitly includes those dependencies—and includes timelines for them.
Another frequent acceptance blocker is unclear performance expectations. Vendors may confirm functional correctness yet not agree on throughput, response times, or concurrency targets. Procurement teams should therefore insist on measurable acceptance thresholds, even if initial targets are conservative and can be tuned later.
Across enterprise IT and operational technology procurement, modernization efforts share similar themes: teams look for improved consistency, reduced manual effort, and smoother scalability. But modern systems also demand stronger operational discipline: configuration governance, monitoring, and clear incident processes.
For procurement teams, this produces a consistent workflow:
This guide is written to support that workflow directly around Havi Nextgen.
To make this context more actionable, buyers often translate operational goals into “measurable outcomes” using a simple structure:
Then the procurement process aligns those outcomes to deliverables. For example, if a primary outcome is error reduction, the implementation plan must include data validation rules, reconciliation steps, and training that reduces operator mistakes. If an outcome is faster approvals, the plan must include integration with identity/authorization workflows and evidence that permissions behave correctly.
In parallel, governance becomes a procurement requirement. Next-generation systems often introduce new configuration layers—permissions, roles, policies, workflows, or automation rules. Procurement teams should ensure the supplier proposal includes governance responsibilities: who owns configuration changes, how changes are reviewed, and how audit evidence is produced.
The table below rephrases “additional important information” into a structured, buyer-friendly comparison. Use it to standardize conversations with suppliers so that quotes are comparable.
| Evaluation area | What to ask supplier | What “good” looks like | Red flags |
|---|---|---|---|
| Scope and deliverables | Which modules are included? What exact deliverables are produced? | Itemized scope + clear deliverables (docs, configs, test evidence) | Scope described vaguely; missing definition of responsibilities |
| Implementation approach | What is the step-by-step rollout plan (phases, timeline, milestones)? | Phased plan with acceptance checkpoints | No milestone-based validation; unclear testing ownership |
| Integration requirements | How does it integrate with our systems? What are the interface assumptions? | Documented integration mapping and verification steps | Assumes “it will work” without interface evidence |
| Support model | What support tiers exist? How are incidents categorized and resolved? | Defined escalation path and responsibilities post go-live | Support described only as “top effort” with no incident process |
| Security and governance | What security reviews are supported? What logging/audit artifacts exist? | Clear security controls and evidence packages | Security left as an afterthought; missing audit/readiness artifacts |
| Training and handover | What training is offered? Who is trained, and what materials are provided? | Role-based training + runbooks and admin guides | Training limited to generic sessions without operational materials |
| Commercial terms | How is pricing calculated? What happens with change requests? | Transparent pricing line items and change-control process | Hidden assumptions; change requests priced unpredictably |
To make this table even more useful, procurement teams can score each supplier response against the “good” description. For example, if a supplier provides a rollout plan but does not specify acceptance checkpoints, you can score “partial” or “not met.” This turns qualitative comparisons into a structured decision.
Additionally, ask suppliers to provide “assumptions” explicitly. Many project disputes occur because one party assumed something else. Good proposals list their assumptions such as:
When these assumptions are documented, procurement can confirm them contractually or address gaps before go-live.
Below is a practical sequence you can use whether you’re working in a large enterprise or a smaller organization. It’s designed to reduce risk in selecting Havi Nextgen by ensuring every decision is tied to measurable requirements.
Write down what success means for your organization. Examples include throughput improvements, fewer manual steps, more consistent reporting, or reduced operational burden. Then capture constraints such as timeline, internal capacity, and governance expectations.
To make this step more concrete, include at least one “operationally verifiable” outcome. For instance:
Constraints should also include non-negotiables like compliance requirements, data residency rules, or strict scheduling windows. When constraints are defined up front, vendors cannot later treat them as optional or negotiable.
Collect details about your current environment—identity management, network constraints, relevant integration systems, and operational tooling. This step prevents “surprise incompatibilities” later.
Consider producing a short “current-state map” that includes systems boundaries and data flows. You don’t need a full architecture document, but you do need enough clarity to answer questions like: What systems will Havi Nextgen talk to? Where does authentication come from? Where do logs need to be stored? What event or data formats are used today?
Procurement teams often help by ensuring that the technical team has access to the right inventory information. For example, the identity provider’s configuration (SSO URLs, group mapping patterns, RBAC constructs), the data stores used by current reporting workflows, and existing monitoring integrations all influence implementation effort.
Ask suppliers to respond in a consistent structure: scope, implementation phases, deliverables, acceptance criteria, support model, and itemized pricing. A standardized request improves apples-to-apples comparison.
When you standardize, you reduce ambiguity and allow faster internal review. It’s also a fairness mechanism: suppliers can’t hide complexity behind differently worded packages. The best templates ask suppliers to explicitly state:
Review the supplier’s project plan for clarity: milestones, test strategy, how issues are handled, and what evidence is provided for acceptance. If the supplier cannot describe the plan at a practical level, you should treat that as a risk signal.
Implementation maturity is often visible in the granularity of deliverables. For example, a mature plan will include details like:
Procurement can also ask for a RACI matrix (Responsible, Accountable, Consulted, Informed) that assigns roles for each phase. If the supplier refuses to clarify responsibility boundaries, that is typically not a good sign.
If possible, conduct a pilot with clear entry/exit criteria. Define what “done” means. Use the pilot to verify integration behavior and operational workflows.
A pilot isn’t just a trial of the software; it’s a trial of operational readiness. When designing pilot success criteria, include items such as:
Pilots also help procurement validate licensing assumptions and usage patterns. If the product is licensed per seat, per device, or per usage tier, a pilot can reveal the true number of users and the real operational load.
Ask suppliers to clarify ongoing costs: support renewal, update cadence, expected operational workload, and any add-on services. Total cost of ownership should include both direct and operational overhead.
Total cost of ownership should be examined across time horizons. Some costs appear during implementation (professional services), while others appear later (support renewals, update testing, integration maintenance, and training refreshers). Procurement teams can request a “cost timeline” that lists expected costs across years, not just during the first rollout.
Also consider the cost of governance activities. Next-generation deployments may require new operational roles: configuration owners, release managers, security reviewers, and monitoring owners. If those roles are not already in place, the supplier plan should include how your organization will be trained and enabled to fulfill them.
Ensure the contract or statement of work includes responsibility boundaries, acceptance steps, change-control rules, and support obligations. A well-written contract is a form of operational safety.
Contract clarity is especially important for acceptance. Procurement should ensure that the contract describes how acceptance is performed, what happens if acceptance criteria are not met, and how timelines are affected by integration dependencies.
Additionally, include terms for change control and pricing logic for changes. Without clear rules, change requests can become a negotiation at the worst possible time—during go-live pressure.
Use this section to confirm prerequisites are explicit rather than assumed. This is particularly important when evaluating Havi Nextgen because operational dependencies often determine real-world performance.
To strengthen this checklist further, procurement teams should also validate operational readiness and governance completeness. Consider adding the following pre-signing checks:
These items matter because many post-contract issues are not “unexpected”; they are simply unmanaged. Turning them into explicit requirements reduces operational conflict later.
Request line-item breakdowns. Compare proposals on included scope, implementation services, support coverage, and acceptance-test deliverables. A lower total can hide extra integration or training costs.
Also request a “scope-to-cost mapping” summary from each vendor. For example, ask them to list which line items correspond to each implementation phase and which deliverables are included. If a vendor cannot map costs to deliverables, you may have difficulty enforcing acceptance later.
Ask for a phased rollout plan with milestones, a test strategy with evidence outputs, named responsibilities for integration tasks, and a documented support and escalation process.
Additionally ask for a risk register and mitigation plan. Delays commonly stem from dependency readiness (environment setup, data quality remediation, identity configuration), and a good supplier will address these dependencies proactively rather than treating them as surprises.
Not always, but a pilot is a common risk reducer when integration complexity is high or when internal teams need time to confirm workflows. Use clear entry/exit criteria to make the pilot decision objective.
Consider a pilot when you need to validate performance under realistic loads, confirm data mapping logic, or test operational workflows with real users. If the pilot will be used as acceptance evidence, ensure the contract references pilot outcomes and defines what happens if pilot acceptance fails.
Acceptance criteria and evidence requirements are key—especially for integration correctness, operational readiness, and measurable performance targets aligned with your outcomes.
Make sure the supplier defines not only “what will be tested,” but also “what evidence will be produced.” For example, integration evidence could include sample transaction logs, interface reconciliation reports, and regression test results.
Standardize your request for proposal (RFP) template, ask for itemized scope, and evaluate supplier maturity using consistent criteria: methodology, documentation quality, support governance, and training completeness.
Fair comparison also involves controlling for assumptions. Ask vendors to list assumptions explicitly. If one supplier assumes your team will do certain integration tasks and another supplier includes those tasks, the comparison can become misleading unless those differences are clearly identified.
No. The technology must match your operational workflow, but deployment success depends on support readiness, change management, governance, and how quickly issues can be resolved post go-live.
In many real projects, the largest operational burden comes from governance gaps. If configuration changes are not controlled, or if monitoring is not established early, operational issues accumulate—leading to higher costs and slower adoption.
Look for sample project plans, evidence of similar integrations, documentation examples, and an outline of how they handle issues during implementation and after launch.
Ask for a “deliverables pack” or examples of documentation they have produced in past implementations: runbooks, admin guides, integration test templates, and training materials. Even if exact content differs, the quality and completeness can be indicative of delivery maturity.
It’s tempting to focus on headline capabilities when researching Havi Nextgen. A more reliable approach is to anchor evaluation on operational outcomes and governance readiness. Practically, this means:
When teams apply these steps, the procurement process becomes calmer and decisions become easier to justify internally.
To keep evaluation objective through the full procurement cycle, consider the following discipline techniques:
Procurement objectivity also benefits from managing stakeholder expectations. Technical teams may want to optimize feature selection, while operations teams want operational stability, while finance teams focus on cost and lifecycle. A disciplined procurement process aligns these groups around shared criteria: deliverables, acceptance, and total ownership costs.
Choosing Havi Nextgen should not be a leap of faith driven by marketing or an isolated quote. Instead, treat the decision as an operational fit assessment: confirm scope, evaluate supplier implementation maturity, model total cost of ownership using itemized assumptions, and formalize acceptance conditions. With a disciplined approach, your organization can move from “interest” to a well-supported deployment plan—backed by clear roles, measurable criteria, and governance readiness.
Ultimately, the goal is confidence. Confidence that the system will be deployed as promised, integrated correctly, supported effectively, and governed responsibly. When procurement decisions are tied to evidence and acceptance—not just product claims—Havi Nextgen can become a stable modernization foundation rather than a source of unresolved risk.
To reinforce this confidence, ensure that the final agreement includes the same structure your procurement evaluation used: clear deliverables, measurable acceptance, defined responsibilities, explicit assumptions, and a support model that matches operational reality. When that structure is present, teams can execute confidently and reduce the likelihood of unpleasant surprises after go-live.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
The Guide to Car Trading
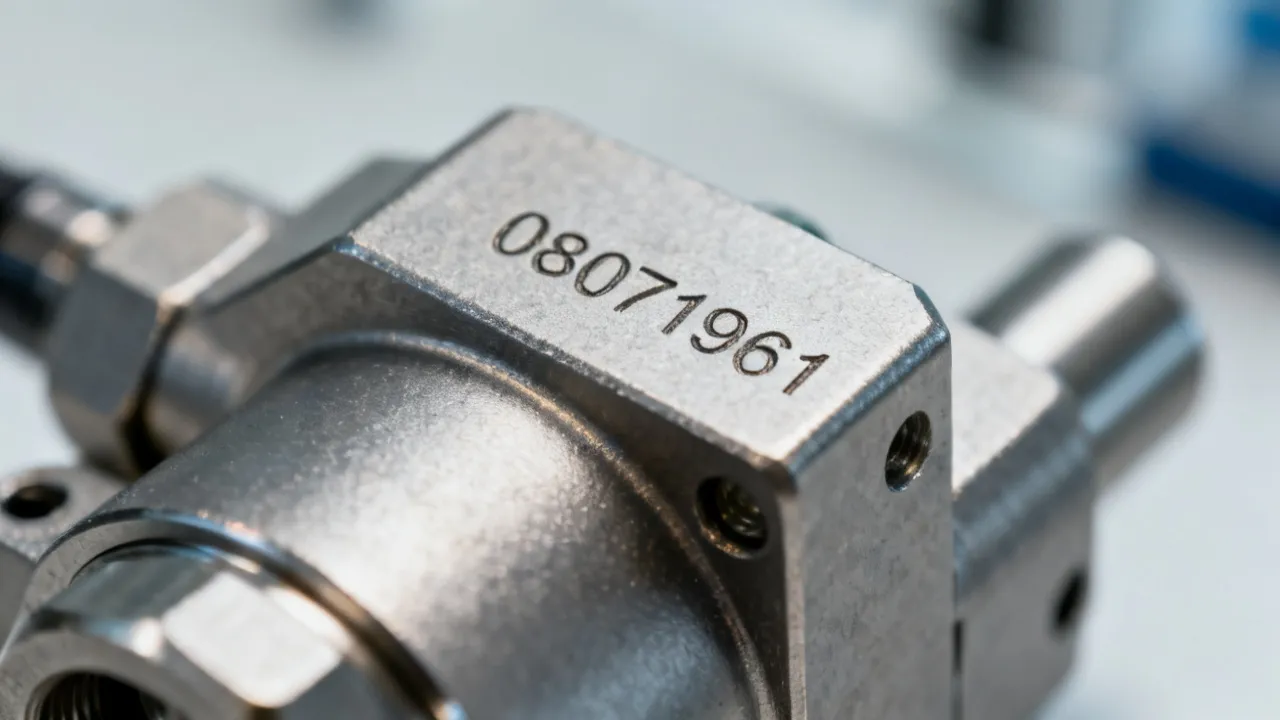
Understanding Product Identifier 08071961 in Supply Chains
This guide explains how product identifier “08071961” functions in procurement, traceability, and quality assurance workflows. It also provides objective background on why such codes matter in manufacturing and logistics, how suppliers validate specifications, and what stakeholders should document to reduce ordering errors, delays, and compliance gaps across nearby operations.
Understanding Sac 2.0 for Modern Security Assessment
Sac 2.0 helps organizations structure security assessment with clearer evidence, repeatable testing, and stronger governance. This guide explains what Sac 2.0 typically emphasizes in practice, how stakeholders align on scope and controls, and why well-defined supplier and documentation workflows matter—covering assessment conditions, expert considerations, and implementation steps in an objective, decision-ready way.
Understanding POC Tcu: Supply, Quality, and Use Cases
This guide explains Poc Tcu in practical terms—what it is, why it matters for performance and reliability, and how procurement decisions affect outcomes. It provides objective background on the keyword “Poc Tcu,” discusses supplier considerations typical for industrial components, and outlines requirements, sourcing checks, and operational conditions in a way that helps readers evaluate fit without hype.
Prisma 1.8: Practical Guide for Informed Software Choices
Prisma 1.8 matters when teams evaluate workflow automation, configuration discipline, and maintainable output across production environments. This guide presents objective background on Prisma 1.8 and the broader category of enterprise tooling, focusing on how organizations assess fit, risks, and operational readiness without relying on unverifiable claims.
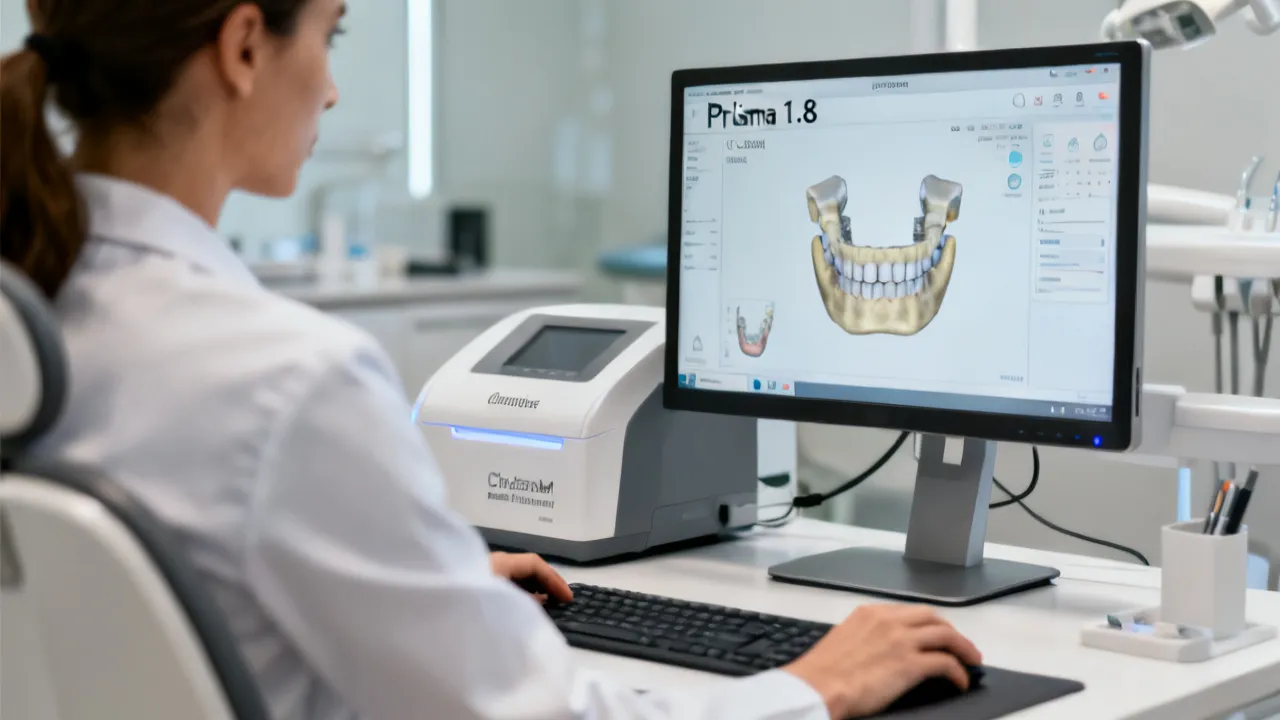
Prisma 1.8 in Dental CAD/CAM: Expert Guide
Prisma 1.8 is a key reference point for teams evaluating dental CAD/CAM workflows, software capability, and production consistency. This guide explains, in objective terms, what versioning such as “Prisma 1.8” typically signals for digital dentistry—linking design, restoration planning, and manufacturing readiness—so clinics and labs can assess fit, risks, and operational requirements.
Understanding Fbde Nexion and Modern Supply Connectivity
This guide explains how Fbde Nexion fits into modern connectivity and supply workflows, with practical buying and evaluation guidance. Objectively, Fbde Nexion is discussed as a network-oriented concept tied to procurement, partner management, and shipment coordination. Readers will learn what to check, how to compare suppliers, and which requirements matter before choosing an implementation path.