This guide explains Kony Dbx in practical, objective terms for teams evaluating integration, performance, and operational fit. Background context covers what “DBX” typically implies in industrial/software workflows, common selection criteria, and how vendors’ documentation and service terms should shape purchasing decisions—without relying on assumptions or marketing claims.
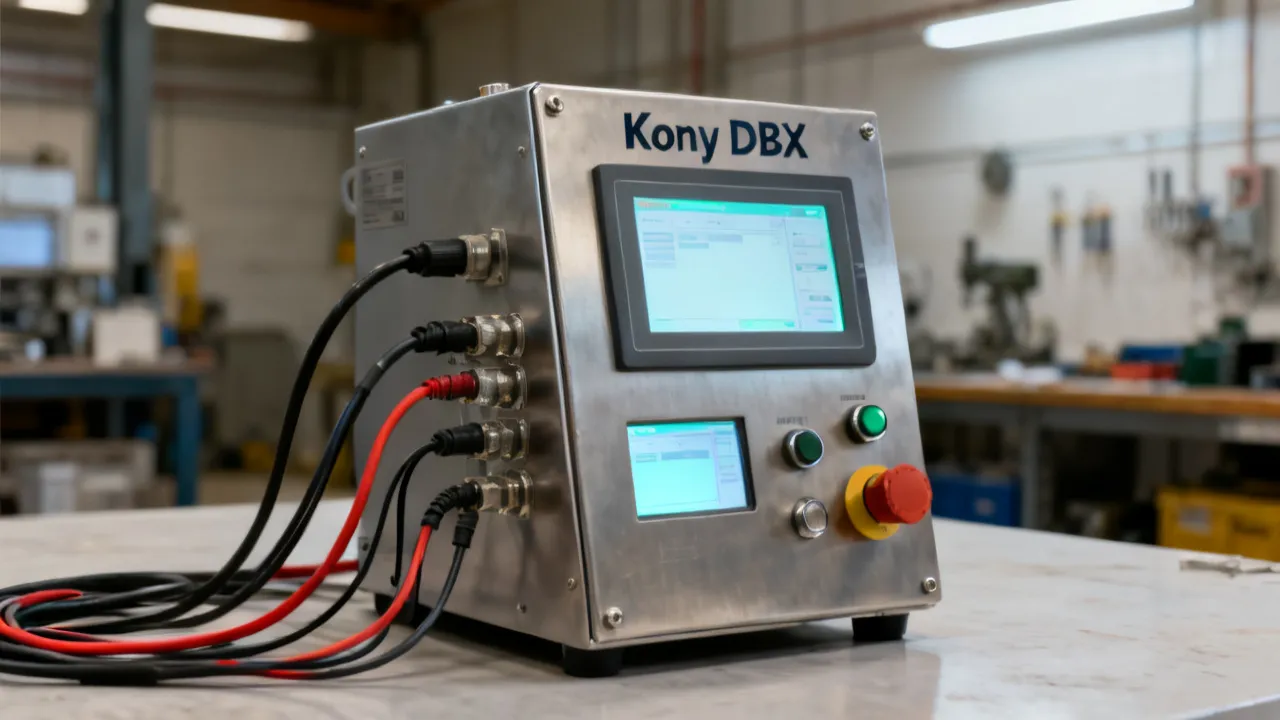
Kony Dbx is best assessed through a disciplined, evidence-based evaluation rather than a single feature list. Professionals typically focus on compatibility with existing architecture, operational risk (including failure modes and recovery behavior), maintainability (configuration lifecycle, upgrade/patch impact, and runbook maturity), and documented performance evidence that aligns with your actual workload. In other words, the right approach is not “which vendor sounds best,” but “which system demonstrably fits your constraints and responsibilities.”
When comparing Kony Dbx against other options, the reliable method is to map your workflow requirements to the vendor’s stated capabilities, confirm integration boundaries, and verify support responsibilities before committing resources. This includes understanding what happens during incident response, who owns which layers of the stack, and how quickly the supplier can help when production conditions deviate from expected states.
Where price, supplier terms, and deployment constraints remain unclear, the decision should pause until requirements, acceptance criteria, and service coverage are explicitly documented. Avoid treating incomplete procurement packages as “good enough,” because the cost of ambiguity shows up later as rework, extended pilots, or stalled releases.
In many engineering and enterprise contexts, abbreviations like “DBX” appear as shorthand tied to a product line, a component family, or an implementation label inside a broader platform. As a result, the term “Kony Dbx” should be treated as a specific system or configuration name that may reference:
Because naming conventions vary by vendor, documentation practices, and region, an expert evaluation should begin with the authoritative documentation associated with the exact model or SKU you intend to purchase. “Kony Dbx” alone is rarely sufficient as a technical identifier. Instead, evaluation must anchor to the exact artifact: SKU, version, deployment topology, licensing model, and any required dependencies.
In real-world procurement, misunderstandings often occur when stakeholders assume that two similarly named components behave the same way. Even small differences—such as runtime version, connector type, supported authentication method, or message schema conventions—can materially affect integration success, security posture, and operational burden.
Therefore, a professional evaluation workflow typically starts with a “definition capture” phase:
It’s common for teams to focus on headline features—especially when timelines are tight. But operational environments reward a different question: fitness-for-use. Fitness means the system behaves predictably under your constraints (data quality, concurrency, network conditions, security posture, maintenance window limits, escalation paths, and operational staffing levels).
For Kony Dbx, treat capability as a set of documented behaviors. Fitness is what happens when those behaviors are exercised against your real workflows. This distinction matters because a system can be “capable” in a demo while still failing in production due to edge-case data, unusual timing relationships, partial outages, or misaligned ownership boundaries.
Responsible procurement and engineering teams handle this by establishing acceptance criteria, integration test plans, and ownership for incident response before deployment. They also build an evaluation strategy that distinguishes:
When capability and fitness are conflated, organizations often overpay for features they don’t need while underinvesting in what truly determines outcomes: integration correctness, operational visibility, and sustainable change management.
An industry expert’s perspective usually highlights integration as the deciding factor. Even when a solution can technically connect to other systems, success depends on details that often get lost in high-level statements. For Kony Dbx, integration success depends on your ability to validate and enforce contracts across upstream and downstream boundaries.
Even if the vendor provides integration connectors, you still need clarity on the following:
When these aspects are missing or only described informally, project risk increases significantly. A robust vendor typically provides not only diagrams but also practical artifacts: sample payloads, test tools, reference configurations, and operational guidance that explains how to interpret real logs and metrics during incidents.
Professional integration assessment goes beyond “it connects” by verifying contract alignment and failure choreography. For example:
In many deployments, the most expensive surprises come from “integration edge cases”: data values that don’t fit constraints, timeouts under specific network conditions, or mismatched expectations about retry behavior that results in duplicate actions.
Beyond initial deployment, maintainability determines good cost. Even when a system meets functional requirements, teams can still face high long-term costs due to operational friction: frequent manual interventions, brittle configuration changes, unclear upgrade procedures, or insufficient role separation.
For systems labeled as Kony Dbx, you should evaluate:
This lens helps prevent hidden “maintenance debt,” where teams spend more time managing exceptions than delivering outcomes. Maintainability also impacts security because operational work often includes manual steps. Manual steps can increase human error, reduce consistency, and complicate compliance evidence collection.
To evaluate maintainability, a professional approach includes asking for artifacts that reflect day-2 operations:
It’s also worth checking whether the platform supports safe operational patterns such as canary releases, feature toggles, or staged configuration rollouts. These patterns reduce risk by preventing a single misconfiguration from impacting all workflows at once.
The request you provided does not include specific price figures, currency, or supplier names. In such cases, top practice is to request a structured quote and compare on comparable terms rather than comparing single-line numbers. If you only compare “annual cost” without context, you risk selecting a plan that appears cheaper but imposes significantly higher operational or implementation costs.
When obtaining a quote for Kony Dbx, ask the supplier to itemize:
In professional procurement, clarity is itself a deliverable. For example, if the quote includes “integration support,” you should clarify whether that support includes writing custom adapters, building test harnesses, or only assisting with configuration and guidance.
Also ensure you compare total cost of ownership (TCO) rather than only license fees. For Kony Dbx, TCO can be affected by:
By forcing the quote to be transparent, your organization reduces decision ambiguity and supports internal approval processes. It also helps you align expectations between procurement and engineering teams so neither side discovers surprises after purchase.
Even without discussing sensitive or speculative claims, compliance and risk assessment are standard in professional environments. You should confirm that the supplier can support your governance needs, including security posture, data handling practices, change management discipline, and operational continuity planning.
While specific requirements vary by industry and region, the following checklist is a practical starting point:
Where applicable, align these checks with frameworks like ISO/IEC 27001 for security management and NIST guidance for software security and risk management. Using recognized frameworks makes your evaluation more defensible to internal audit teams and helps ensure you don’t miss critical control areas simply because they weren’t emphasized in product documentation.
In addition to the checklist, professionals often request evidence artifacts rather than verbal assurances. Evidence might include:
When evidence is limited, you can still proceed—but you should adjust risk posture accordingly: tighten pilot scope, strengthen monitoring, and require additional review steps before scaling up.
Across enterprise and industrial software, modules that resemble “DBX” labels often appear as part of a larger integration or data exchange strategy. Typically, such components help normalize, route, and transform information between systems that may have different models, schemas, and operational expectations.
Common usage patterns include:
However, the only dependable conclusion is the vendor’s own technical specification for the exact Kony Dbx item you are considering. Generic descriptions should be treated as preliminary leads, not as final truth.
When you evaluate Kony Dbx within an industry context, a useful approach is to identify where it sits in your end-to-end flow. For example, ask:
These questions help prevent a common misconception: assuming that a component’s label (or marketing story) reflects actual runtime behavior. Runtime behavior is what determines reliability, compliance evidence generation, and operational load.
To evaluate Kony Dbx responsibly, perform tests that mimic your production behavior patterns. The goal is not merely “it works,” but “it works safely and measurably.” A solid test approach often includes functional validation, resilience testing, performance profiling, observability verification, and security review.
Even when a vendor offers a pilot, your organization should treat the pilot as a structured experiment with measurable criteria. Without criteria, pilots become expensive demos that do not inform decision-making under operational risk.
A mature test plan frequently includes the following categories:
For performance-related claims, rely on documented results from official vendor materials or third-party evaluations when available. But also recognize that vendor benchmarks are rarely identical to your environment. Use vendor numbers as starting points, then validate with your own tests to establish confidence.
When testing, professionals also define what “good” looks like for failure behavior. For example, you may specify:
This turns performance and reliability from vague assertions into measurable outcomes. It also reduces disagreements later about whether a failure was “within tolerance.”
The table below offers a structured comparison of common implementation pathways for systems in the Kony Dbx category. It is phrased as a decision aid (not as an endorsement of any single vendor approach). Replace “Kony Dbx” with your specific SKU documentation where applicable.
| Evaluation dimension | Option A: Standard integration | Option B: Custom integration | Option C: Phased rollout |
|---|---|---|---|
| Primary goal | Deploy using documented interfaces | Optimize mappings/workflows beyond defaults | Reduce risk by introducing scope incrementally |
| Typical inputs needed | Vendor specs, sample payloads, config templates | Extended mapping rules, engineering resources, acceptance tests | Use-case prioritization, environment readiness plan |
| Requirements clarity | Lower ambiguity if interfaces are fully documented | High clarity needed for custom behavior and edge cases | Clear stage gates and rollback criteria are required |
| Change management | Veryly configuration-level updates | Includes code/config extensions and version coordination | Requires disciplined release planning |
| Operational risk | Moderate; depends on data quality | Potentially higher if requirements are incomplete | Lower per stage if acceptance gates are enforced |
| Top fit when | Your workflows match vendor-supported patterns | You have unique workflows but can invest in testing | You need continuity and cannot tolerate large cutover risk |
To use the table effectively, teams often add an extra dimension that isn’t always shown: organizational readiness. For example, even if Option B (custom integration) appears necessary, the organization must confirm it has the engineering capacity to maintain it, the security review capacity to approve custom code or configurations, and the operations capacity to monitor and troubleshoot it.
To keep evaluations objective, use evidence standards rooted in widely used governance practices. For security and risk management, organizations often align with ISO/IEC 27001 and related NIST guidance (e.g., NIST SP 800 series). For performance and reliability engineering, teams frequently reference ISO/IEC/IEEE standards for systems and software testing practice. For procurement discipline, internal audit frameworks commonly require itemized scopes, documented acceptance criteria, and verifiable deliverables.
Practical note: If your supplier provides only marketing summaries and no technical artifacts, request at least one of the following: integration diagrams, API schemas, test plans, sample logs, or a security/architecture overview. Those artifacts are typical expectations in mature vendor ecosystems, and they also help you build your internal plan for testing and operational readiness.
In mature due diligence, “evidence” is not limited to documents. Evidence can include:
When a vendor cannot supply evidence, you can still proceed if the risk is acceptable—but you must compensate elsewhere. Compensation might include a stronger internal pilot, additional independent testing, and tighter contractual controls that require the vendor to remedy identified gaps.
Professional organizations also document assumptions. For example, if you assume that logs include correlation IDs, then validate it during pilot. If it fails, the assumption becomes a documented risk and a contractual mitigation requirement.
For additional rigor, teams often add two supporting steps: (1) a data quality assessment of the input systems and (2) a change-management rehearsal for release day. These steps reduce the chance that the solution fails due to upstream data inconsistencies or due to operational processes that were never rehearsed.
In addition to these, professionals commonly insist on operational constraints being addressed in writing—such as maintenance windows, maximum downtime tolerance, and backup/recovery procedures. Without these constraints, teams often discover during rollout that they can’t meet their operational schedule, even if the technology is otherwise correct.
Kony Dbx refers to a specific named product, component, or configuration used within a broader system context. Because “DBX” can vary by vendor, you should confirm the exact definition in the official technical documentation for the specific SKU you are evaluating. The correct identification includes version, deployment topology, and any required dependencies or included connectors.
Compare by documented integration interfaces, error handling behavior, observability outputs, upgrade path, and support terms. Avoid relying only on feature lists; instead, compare deliverables and acceptance criteria you can test. A useful comparison includes how each solution behaves when inputs are malformed, when dependencies are slow, and when security controls fail closed.
Performance matters, but operational outcomes also depend on resilience, correctness, and maintainability. An expert evaluation treats performance as one dimension in a wider risk-and-fitness framework. For example, a highly performant system that fails unpredictably under network partitions may still be a poor fit for production reliability.
Typical expectations include interface specifications (schemas/contracts), admin guides, operational runbooks, security/architecture overviews, sample logs, and—when available—test reports or benchmark methodology. You may also request sample payloads, error code catalogs, and deployment diagrams that match your planned topology.
Start with a test matrix covering your top workflows and edge cases. Use a pilot environment and require measurable acceptance criteria. Validate logs and failure handling early so troubleshooting doesn’t become a discovery process during production cutover. “Quickly” in professional settings usually means focusing on the highest-risk workflows and integrating observability from day one.
Request an itemized quotation aligned to scope, environments, support coverage, and documentation deliverables. If key details cannot be provided, consider delaying decisions until the procurement package is complete. If you must proceed due to business urgency, contractually require milestone-based deliverables and acceptance criteria tied to pilot results.
Frequent issues include unclear interface contracts, insufficient observability for operations teams, incomplete edge-case testing, and ambiguous support responsibilities during incidents. Another common reason is insufficient rehearsal of operational processes: teams install the technology but do not practice monitoring, escalation, and rollback procedures.
Implementation is often affected by your organization’s local infrastructure, security policies, and change-management culture. While the product name itself doesn’t guarantee location-specific behavior, your operational procedures and compliance obligations will vary and should be reflected in the rollout plan. Also consider localization of support processes, language requirements in logs/runbooks, and data residency constraints when relevant.
Ask how Kony Dbx handles schema evolution: does it tolerate unknown fields, how does it behave when data types change, and are there versioned interfaces? Also ask what validation happens prior to processing and how invalid data is surfaced—blocked, quarantined, or transformed with defaults. A professional evaluation includes testing schema drift scenarios, not just stable schemas.
Define incident ownership explicitly: what constitutes a vendor responsibility (platform defects, known issues, connector bugs) versus what remains your responsibility (input data problems, integration configuration mistakes, upstream system outages). Confirm escalation procedures and required evidence formats (log extracts, correlation IDs, timestamps). Then test ownership during the pilot by simulating failures and following the escalation path.
Kony Dbx should be evaluated with a professional mindset: define requirements, demand authoritative documentation, test integration behavior under realistic conditions, and verify support and upgrade policies before final procurement. This approach reduces uncertainty, supports internal governance, and produces outcomes that can be defended with evidence rather than assumptions.
Most importantly, success depends less on the existence of “features” and more on the operational fit: how the system behaves under stress, how quickly it can be diagnosed, and how sustainably it can be changed over time. When you evaluate Kony Dbx through capability plus fitness, and when you treat integration and maintainability as primary decision drivers, you substantially improve your chances of achieving production outcomes without incurring avoidable maintenance debt.
Next step: If you share the exact Kony Dbx model/SKU and your intended environment (integration endpoints, data formats, and support expectations), a tighter assessment framework can be tailored to your use case—still using objective, verifiable criteria.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
Understanding 60817674500: Pricing, Supplier Signals, Quality Steps
This guide explains how to interpret the numeric keyword 60817674500 in procurement contexts, how pricing is commonly structured, and what supplier information should be verified before ordering. Objectively, it discusses what such identifiers often represent, why supplier traceability matters, and which due-diligence steps reduce delivery and compliance risk.
822478979788877878878897979797 Buyer’s Guide
This guide explains how to evaluate 822478979788877878878878897979797 procurement decisions with an objective lens. It outlines what the code typically signals in supply-chain workflows, how to verify supplier readiness, and which due-diligence steps reduce risk. You’ll also find a comparison framework, requirements, and practical FAQs for informed purchasing.
PrismaJOY Buying Guide: Requirements, Suppliers, and Pricing
PrismaJOY is a structured solution-focused product guide aimed at helping buyers evaluate sourcing, pricing factors, and implementation readiness. Objectively, PrismaJOY is discussed in terms of how “JOY” features map to selection criteria, compatibility, and supplier support in day-to-day procurement and deployment workflows, emphasizing due diligence and documented requirements.
PrismaJOY Guide: Pricing, Suppliers, and Buying Conditions
This guide explains how to evaluate PrismaJOY for responsible purchasing decisions, focusing on pricing structure, supplier credibility, and practical requirements. Objectively, PrismaJOY is presented as a brand name associated with consumer products, while “supplier” refers to the distribution chain that impacts delivery, warranty handling, and service responsiveness.
How Multishop Streamlines Modern Multi-Vendor Selling
This guide explains how Multishop supports multi-vendor commerce by connecting catalogs, orders, and supplier workflows in a single operational view. In objective background terms, multi-vendor platforms exist to reduce duplication of product and fulfillment management, while improving governance through standardized pricing rules, inventory updates, and supplier controls.
Understanding Gordo9498416253t and Related Product Options
This guide explains how to evaluate Gordo9498416253t-type listings and nearby supply options, focusing on how buyers can verify pricing, supplier credibility, and compatibility before purchase. Objectively, the keyword “Gordo9498416253t” functions as a listing identifier-like term, while “related product options” reflects the broader need to compare sellers, documentation, and performance claims using reliable sourcing and practical checks.